


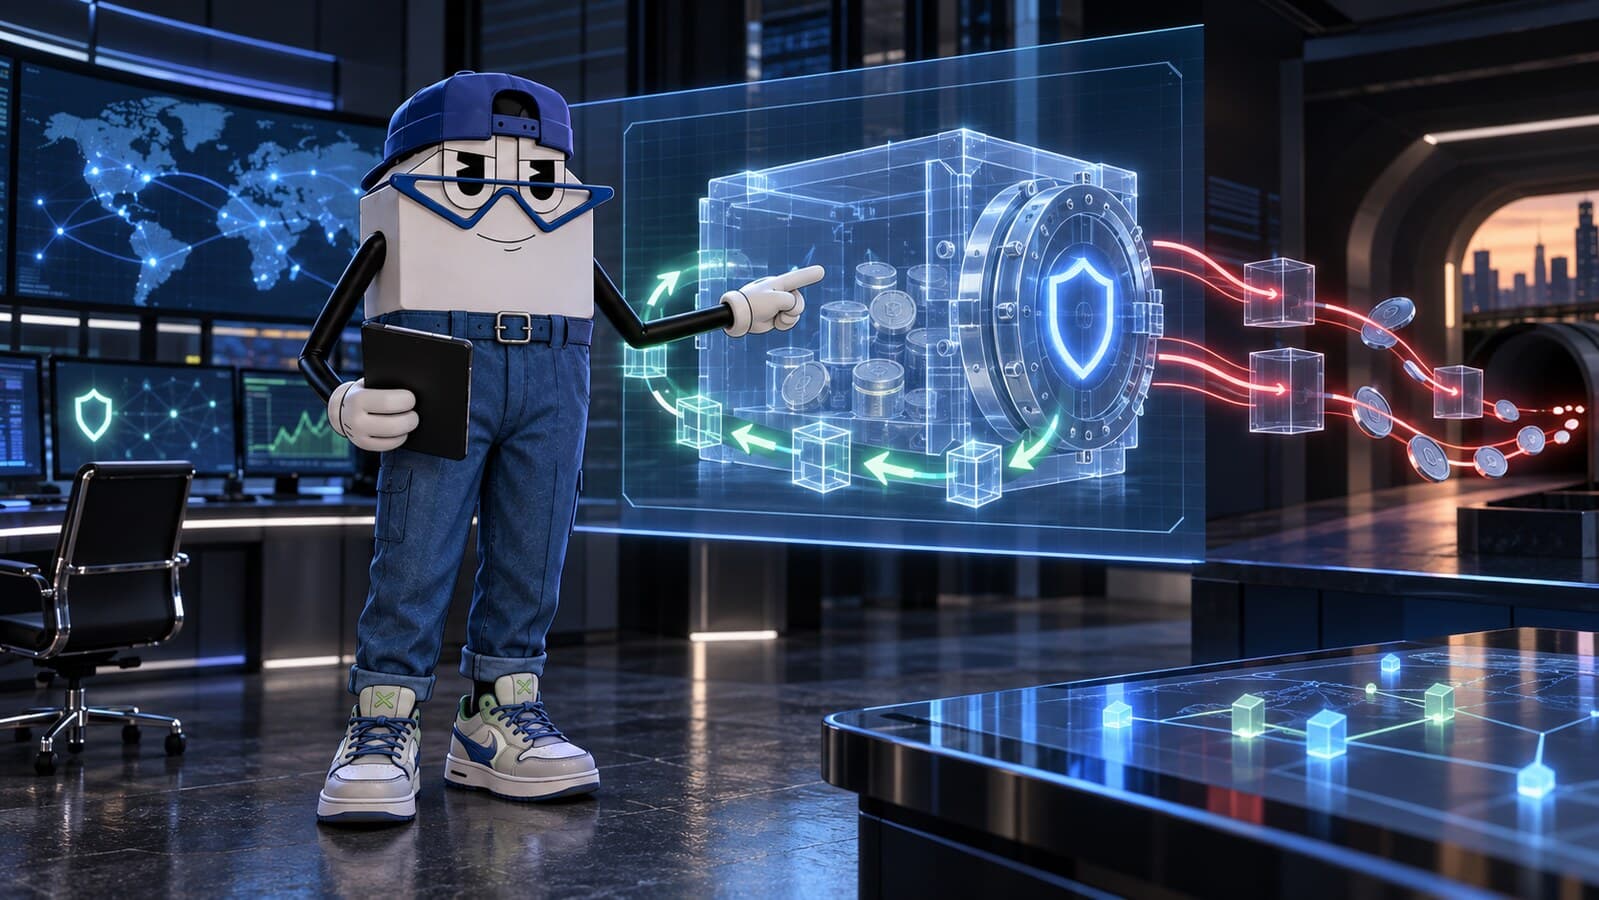
Cronos’ official postmortem says an attacker used manipulated TONIC collateral to borrow $120.4 million across nine Tectonic markets. A validator-backed chain rollback reversed approximately $111.2 million, but $9.19 million had already left Cronos and remains unrecovered.
The new figures materially change the scale of the incident first reported in late August. Early estimates placed the exploit near $75 million. The postmortem now describes a much larger borrowing event, an emergency network halt and a rollback that removed nearly two hours of blockchain history.
The distinction matters: this was not an attack on the Bitcoin network or the Crypto.com exchange. The incident centered on Tectonic, a lending protocol deployed on Cronos, and the response was coordinated at the Cronos network level.
Key Findings
- The attacker borrowed $120.4 million from nine Tectonic markets after manipulating the price of thinly traded TONIC collateral.
- Cronos validators halted the network and rolled it back, reversing about $111.2 million of the unauthorized borrowing.
- Approximately $9.19 million had already moved off Cronos before the halt and remains unrecovered.
- The rollback discarded 10,961 blocks, representing roughly one hour and 54 minutes of chain history.
- Legitimate transactions inside the rollback window were also reversed, turning the incident into a debate about collateral design, network governance and transaction finality.
What the Cronos Postmortem Changed
According to Cronos’ official incident postmortem, validators halted block production after detecting the Tectonic exploit. The network response allowed most of the affected borrowing to be reversed, but only after funds had already crossed out of the chain.
The official accounting puts the total unauthorized borrowing at $120.4 million, with $111.2 million reversed and $9.19 million unrecovered. That supersedes the lower preliminary estimates circulated while the incident was still unfolding. Independent coverage of the completed postmortem also notes that the rollback affected unrelated transactions inside the discarded block window.
How the TONIC Collateral Attack Worked
The exploit appears to have depended on a familiar DeFi weakness: a low-liquidity asset was accepted as collateral at a value that could be manipulated faster than the lending system could respond. The attacker raised the observed price of TONIC, deposited it as collateral and borrowed liquid assets against the inflated valuation.
Bitquery’s transaction analysis identified borrowing across all nine Tectonic markets in a concentrated sequence of transfers. This meant the protocol’s exposure was not limited to one pool: the manipulated collateral became a gateway to drain multiple available assets.
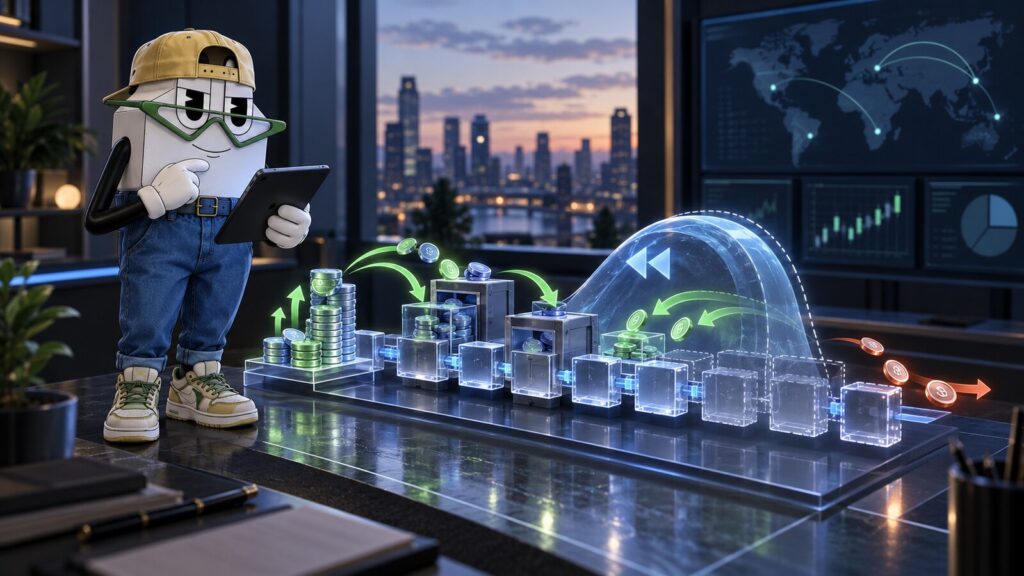
The core lesson is not simply that an oracle produced a bad number. Lending markets must consider whether a collateral asset has enough genuine market depth to support reliable liquidation and pricing. A token can meet a nominal collateral-factor rule while still being too illiquid to absorb stress safely.
Why the Rollback Recovered $111.2 Million
A blockchain rollback instructs validators to resume from an earlier accepted state, effectively discarding subsequent blocks. Because most of the borrowed assets had not yet escaped Cronos, reverting the relevant chain history restored approximately $111.2 million to the pre-exploit state.
The intervention was economically effective, but it was not a conventional protocol-level recovery. It relied on validator coordination and changed the final settlement history of the chain. That makes the response fundamentally different from freezing a single smart contract, pausing one lending market or recovering assets through liquidation.
What the Rollback Cost Other Users
The rollback removed 10,961 blocks—about one hour and 54 minutes of activity. Every transaction inside that window was discarded, including legitimate transfers and contract interactions unrelated to Tectonic.
Those users did not necessarily lose funds permanently, because transactions could be submitted again after the network resumed. Still, the reversal creates operational costs: trades may execute at different prices, time-sensitive actions may expire and cross-chain transfers can require reconciliation. Applications and exchanges connected to Cronos may also need to review deposits or withdrawals around the affected block range.
The Finality Question
The most important market-structure question is whether users can treat confirmed Cronos transactions as final during an emergency. Validators chose to protect a large pool of assets at risk, but doing so showed that sufficient coordination can replace an already-produced chain history.
That trade-off is not unique to Cronos. Networks with concentrated validator sets, emergency governance powers or upgrade controls face the same tension: fast intervention can reduce losses, while intervention itself can weaken expectations of neutral settlement. The quality of the decision depends on transparent criteria, narrow execution and a complete public accounting afterward. A useful comparison is TCP’s Liquid Network federation-wallet analysis, where a Bitcoin sidechain halted activity after a major reserve movement without changing Bitcoin mainnet history.
What Remains Unresolved
The immediate financial question is whether the remaining $9.19 million can be traced, frozen or returned. The longer-term questions are more structural: why TONIC was accepted under the existing collateral parameters, whether pricing safeguards were adequate and what changes will prevent another thin-market asset from creating system-wide exposure.
Tectonic users should rely on official protocol and Cronos channels for recovery instructions. Unsolicited “refund,” wallet-validation or account-recovery messages should be treated as likely phishing attempts. No legitimate recovery process should require a seed phrase or private key.
The Bottom Line
Cronos recovered most of the value affected by the Tectonic exploit, but the mechanism matters as much as the amount. The official postmortem turns the incident into two stories at once: a $120.4 million failure in DeFi collateral controls and a network-level decision to reverse nearly two hours of finalized activity.
The remaining $9.19 million is the unresolved loss. The larger question for users and developers is what safeguards can reduce the need to choose between preserving transaction history and rescuing funds after a protocol failure.
Responses (0 )