


Updated September 18, 2026: Chainflip has restored its cross-chain network after patching the vulnerability behind the September 12 TRON USDT exploit. The incident is now marked resolved, and validators have approved Proposal 008, a recovery plan designed to make affected TRON USDT liquidity providers whole using recoverable TRON USDT and a 1:1 USDC credit for the remaining shortfall.
Chainflip halted its cross-chain network after a flaw in its handling of TRON transaction memos allowed an attacker to trigger duplicate payments from the protocol's vaults. Chainflip's analysis says six unauthorized payouts removed 736,442.17 USDT.
The attack occurred on September 12. Chainflip subsequently patched the vulnerability, carried out a network upgrade and restored the protocol. Its status page marked the incident resolved on September 17.
The incident was isolated to Chainflip's TRON USDT integration. Chainflip has not reported a compromise of the TRON blockchain, Tether, the USDT smart contract or Tether's reserve system.
Key Findings
- Chainflip's analysis attributes 736,442.17 USDT in losses to six unauthorized payouts generated through its TRON memo-processing flow.
- The attacker tested the method eight times over roughly 90 minutes, beginning with small amounts and approximately doubling the size of later attempts.
- Chainflip says the vulnerability has been patched. The protocol was restored through a network upgrade, and the incident was marked resolved on September 17.
- On September 18, Chainflip announced that Proposal 008 had passed with 91 of the 128 authority-set nodes voting in favor, equivalent to 71.09% of the full authority set.
- The approved recovery plan uses recoverable TRON USDT plus a 1:1 USDC credit for the remaining shortfall so affected TRON USDT liquidity provider accounts can be made whole.
What Happened?
Chainflip disclosed the incident on September 13 after investigating failed USDT payouts from the preceding day. According to the protocol, the activity occurred between 01:44 and 03:10 UTC on September 12 and targeted the way its systems interpret swap instructions attached to TRON transactions.
The protocol detected the incident after later USDT payouts began to fail. It then suspended network activity, investigated whether other assets or integrations were exposed and began preparing a controlled restart.
How the Duplicate-Payout Exploit Worked
Chainflip uses transaction memos to read swap instructions attached to transfers on TRON. Most other blockchains supported by the protocol use dedicated contract functions for those instructions, making the TRON integration a distinct processing path.
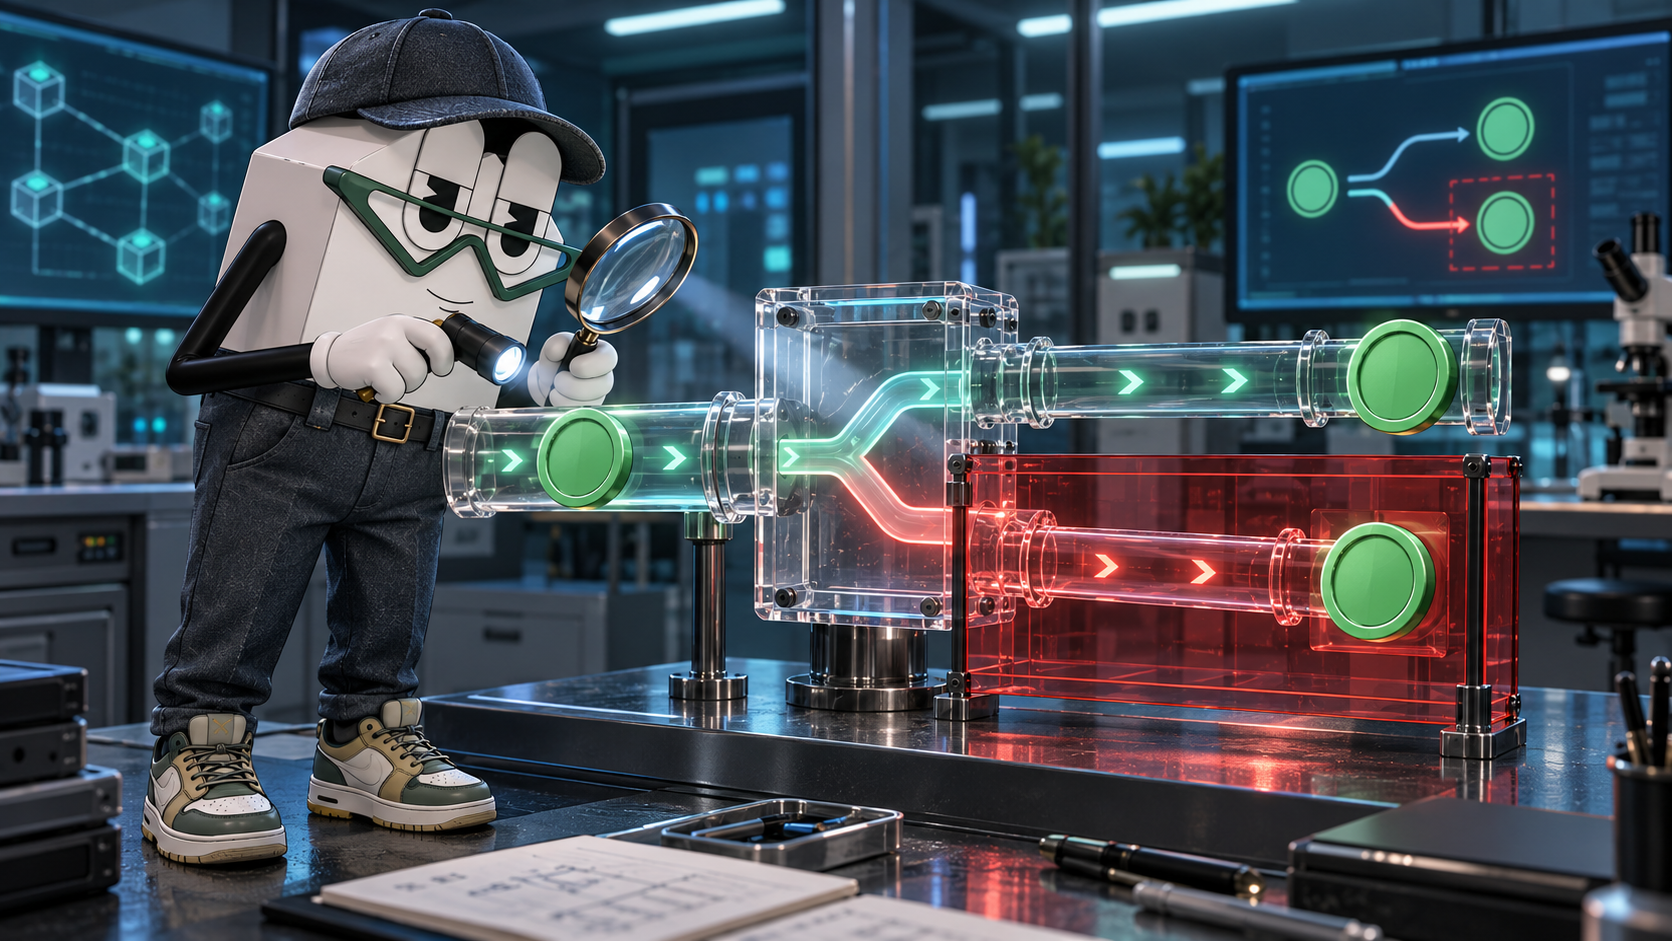
According to Chainflip's post-incident explanation, the attacker took a fetch transaction that Chainflip validators had already signed, submitted it to the vault and attached a malformed memo. The protocol's witnessing layer interpreted that memo as a failed swap and issued a refund on top of the attacker's normal liquidity provider withdrawal.
The result was a double payment against the same underlying transaction flow. The attacker repeated the method eight times over approximately 90 minutes. Six attempts produced unauthorized payouts totaling 736,442.17 USDT.
How Chainflip Patched the Vulnerability
Chainflip said on September 15 that the vulnerability had been patched by tightening the conditions under which its TRON integration reads a transaction memo as a swap instruction.
Before the fix, Chainflip could read a memo from a transaction that moved funds into the TRON vault even when the transfer was wrapped inside another contract call. That behavior allowed a memo attached to a Chainflip-signed transaction to be interpreted in a way that could generate an additional refund.
Under the patched behavior, Chainflip said a memo is read as a swap instruction only when it accompanies a plain TRX transfer or a direct TRC-20 token transfer. Transfers wrapped inside another contract call are excluded, preventing a memo attached to a Chainflip-signed transaction from creating a new swap or refund through the same mechanism.
Chainflip noted that the stricter rule affects the design space for smart-contract wallets or aggregators that send TRON transfers through their own contracts, although it said none of its integrations were using that method at the time of the update.
What the Loss Figure Covers
Chainflip continues to identify 736,442.17 USDT as the amount taken through six unauthorized payouts. The figure comes from Chainflip's own incident analysis rather than an independent audit.
The original September 13 incident report separately identified a legitimate user swap worth 115,654.41 USDT that could not be paid while the network was paused. Chainflip said those funds remained in the vault and could be processed after restart, so that amount was not included in the reported exploit loss.
Chainflip has also said it flagged the exploited funds with relevant parties and would continue trying to recover proceeds. Its later recovery plan states that anything recovered from the attacker can be used to rebuild protocol surplus or a network support fund.
Chainflip Restored the Network After the Upgrade
Chainflip's September 15 restart plan called for a runtime upgrade to handle accounting adjustments and stuck refunds, followed by an engine upgrade containing the exploit fix. Services would then be brought back online once the validator network had reached the required state and Chainflip was satisfied with network stability.
That recovery process has since progressed beyond the paused state described in the original version of this article. Chainflip's official status page now classifies the TRON USDT exploit as resolved and says the protocol was restored through a network upgrade. The incident status changed to resolved on September 17.
This distinction matters because the original September 13 report described a network that was still paused and a restart process that had not yet been completed. Those statements remain part of the incident timeline, but they no longer describe Chainflip's current operational status.
Proposal 008 Approved the LP Recovery Plan
The financial recovery plan also moved from an unresolved question to an approved governance decision. On September 18, Chainflip announced that Proposal 008 had passed, authorizing the use of surplus assets held in protocol vaults to cover the shortfall affecting TRON USDT liquidity providers.
Chainflip reported that 91 of the 128 nodes in the authority set voted in favor, representing 71.09% of the full set. Another 18 nodes abstained and 19 did not respond.
Under the approved plan, each affected liquidity provider is to receive a balance update consisting of whatever TRON USDT can be recovered from the vault plus a 1:1 USDC credit for the remaining amount owed. Chainflip said only USDC would be used to cover the remaining shortfall and that FLIP, ETH and other vault assets would not be used for that purpose.
Chainflip described the funding source as protocol surplus: assets held in protocol vaults beyond amounts reflected as being owed through state-chain accounting. The protocol said these balances can include excess funds arising from gas-fee interactions, deposits to expired channels, incorrect transfers and other funds for which no clear return route or claimant has been established.
The governance approval changes an important part of the original incident story. On September 13, Chainflip was still analyzing how affected users would be made whole. As of September 18, a specific recovery mechanism had been approved by the validator authority set.
What Users Should Know Now
- The September 12 exploit is no longer classified by Chainflip as an active unresolved network incident. Its official status page marks the incident resolved.
- The vulnerability that enabled the duplicate-payout mechanism has been patched, according to Chainflip.
- Affected TRON USDT liquidity providers now have an approved recovery mechanism under Proposal 008 rather than an unspecified future compensation process.
- Users should continue to rely on official Chainflip interfaces and communications for account-specific recovery information and should treat unsolicited reimbursement or wallet-support messages as suspicious.
- Never share a seed phrase, private key or wallet-recovery information with anyone claiming to process a refund or compensation payment.
What the Incident Did — and Did Not — Affect
The evidence continues to support a narrow description of the incident: a vulnerability in Chainflip's handling of TRON transaction memos enabled duplicate payouts from a Chainflip vault.
That is materially different from saying that TRON itself was compromised or that USDT's smart contract or Tether's reserve system was hacked. Chainflip's incident reports describe the failure as occurring within its own TRON integration and payout logic.
The recovery also does not erase the original exploit. Chainflip still reports 736,442.17 USDT taken through the six unauthorized payouts. What changed after the initial disclosure was the operational and governance status: the vulnerability was patched, the network was restored, the incident was marked resolved and a specific mechanism for making affected liquidity providers whole was approved.
What Comes Next
With the network restored and Proposal 008 approved, the story has moved from immediate containment toward implementation of the recovery plan and longer-term security hardening.
Chainflip has said it is reviewing memo handling across the chains it supports, adding monitoring for duplicate payouts and reviewing its broader security practices. It also said recovered exploit funds would contribute to rebuilding surplus or network support resources.
Future material developments could include additional technical findings, recovery of exploited funds or further details about implementation of the approved LP recovery mechanism. Those developments should be distinguished from the facts already established: the September 12 vulnerability has been patched, the protocol has been restored and Proposal 008 has passed.
Primary Sources & Data
- Chainflip — Incident Report: TRON USDT Exploit: Provides the original September 13 account of the exploit, reported loss, attack sequence, pending legitimate swap and initial recovery status.
- Chainflip — Getting Chainflip Back Up and Running: Explains the patched memo-processing behavior, restart sequence, TRON USDT accounting treatment and initial LP recovery framework.
- Chainflip Status — Incident History: Records the TRON USDT exploit as resolved and states that the protocol was restored through a network upgrade.
- Chainflip — Proposal 008 Passed: Making TRON USDT LPs Whole: Provides the validator vote result and the approved recovery mechanism using recoverable TRON USDT and a 1:1 USDC credit for the remaining shortfall.
- Chainflip official X announcement, September 13, 2026: The original announcement is embedded above and documents the incident during its initial response phase.
Sources & Methodology
This report prioritizes Chainflip's official incident reports, restart documentation, governance update and status page. The 736,442.17 USDT loss figure remains attributed to Chainflip rather than presented as an independently audited amount. The article distinguishes the September 13 historical state of the incident from later developments on September 15–18 and separates the confirmed Chainflip integration failure from unsupported claims about the TRON blockchain, Tether or USDT reserves.
Update note: This article was materially updated on September 18, 2026 to reflect Chainflip's vulnerability patch, network restoration, resolved incident status and the passage of Proposal 008. The original incident chronology and reported loss figure have been retained where they remain relevant and supported.
Responses (0 )