


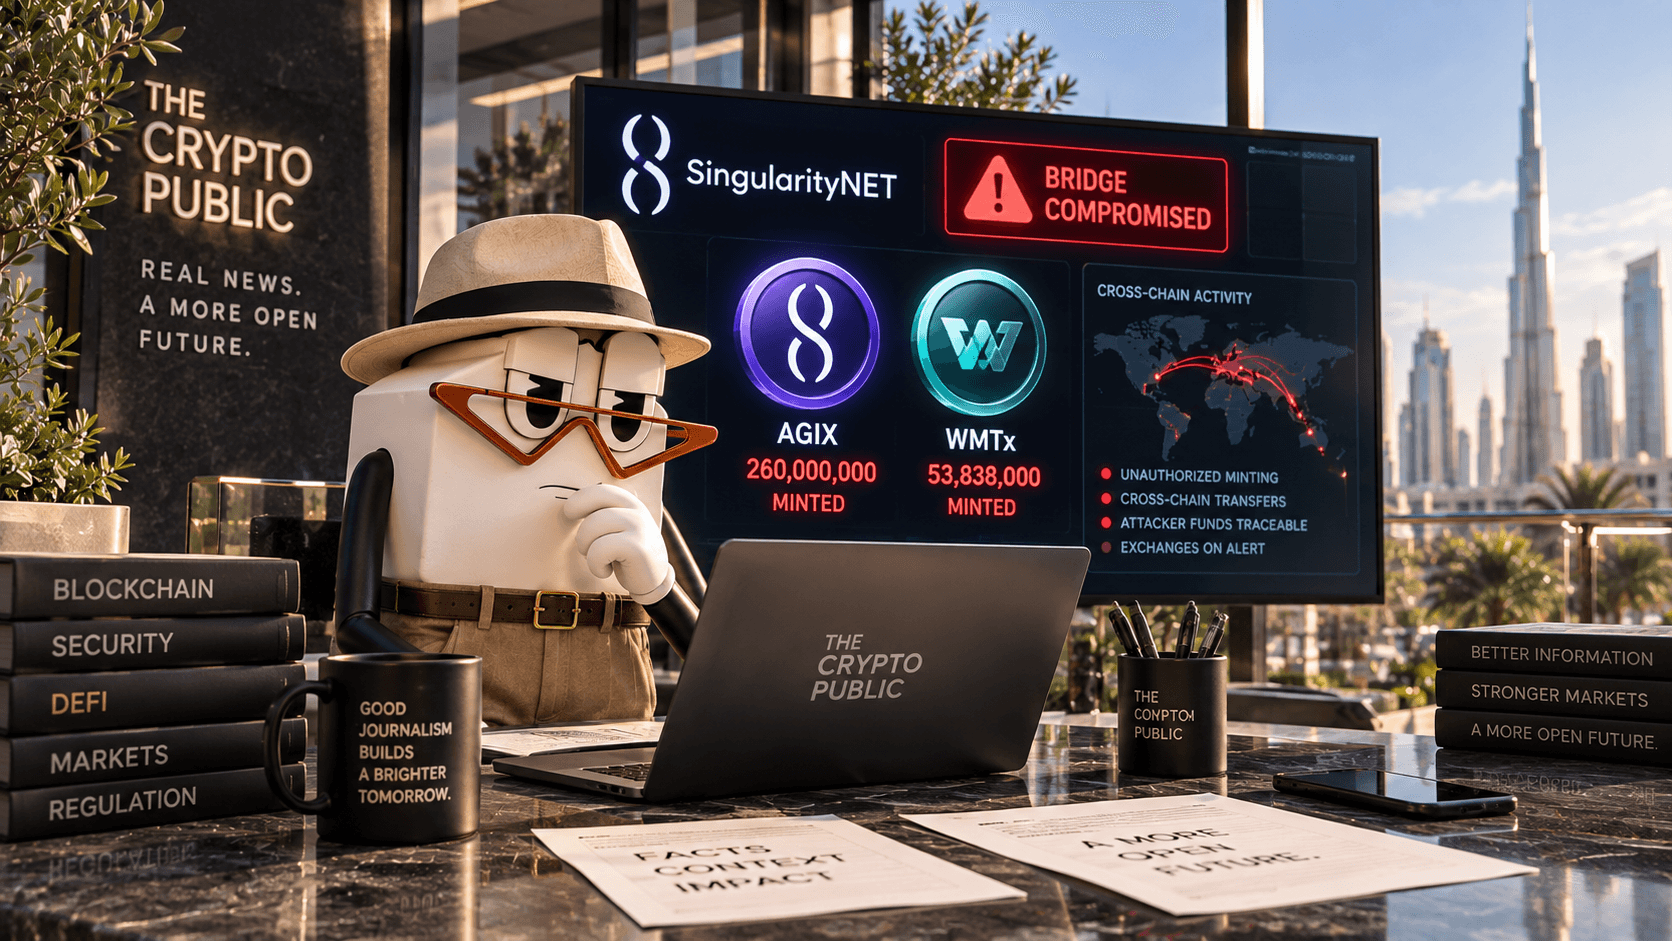
A security incident involving SingularityNET's cross-chain infrastructure has widened across several connected crypto projects, with unauthorized token issuance affecting AGIX, WMTx, NTX and CGV alongside an earlier movement of approximately 8.72 million FET.
Fetch.ai says its own contracts are not currently under threat and has identified SingularityNET contracts — particularly infrastructure associated with the Ethereum–Cardano bridge — as central to the incident. The available evidence points to compromised authorization rather than a failure of Ethereum or Cardano themselves.
Key Findings
- The security incident has expanded well beyond the initial FET and NTX activity, with unauthorized issuance involving AGIX, WMTx and CGV also linked to the attacker cluster.
- Fetch.ai says its own contracts are not currently under threat and has pointed to SingularityNET infrastructure as central to the compromise.
- On-chain analysis measured approximately 895.96 million AGIX, 500.48 million WMTx, 408.53 million NTX and 492.40 million CGV created during the incident, alongside approximately 8.72 million FET removed from a conversion contract.
- The unauthorized token amounts should not be converted mechanically into a headline loss figure because newly minted supply is not equivalent to realized proceeds.
- The incident concerns bridge, token and authorization infrastructure; current evidence does not establish a compromise of Ethereum or Cardano consensus.
- Investigation and recovery remain ongoing, and a final technical post-mortem has not yet reconciled the complete impact across the affected projects.
What Happened?
The incident began drawing attention on September 19 through activity involving Fetch.ai and NuNet. Approximately 8.72 million FET left a Fetch.ai conversion contract, followed roughly half an hour later by the creation of approximately 408.53 million NTX.
The scope subsequently widened as investigators linked additional unauthorized token issuance to the same attacker cluster. Bitquery's on-chain investigation reconstructed activity across FET, NTX, AGIX, WMTx and CGV and measured approximately 2.3 billion token units minted or drained across the five affected assets during September 19–20.
Fetch.ai subsequently said its own contracts were not currently under threat and identified SingularityNET contracts, particularly infrastructure associated with the Ethereum–Cardano bridge, as central to the attack. That clarification materially changed the attribution of an incident that initially appeared to center more heavily on Fetch.ai and NuNet.
The SingularityNET Bridge Is Central to the Incident
The SingularityNET bridge provides cross-chain transfers between Ethereum and Cardano. According to SingularityNET's official bridge documentation, supported assets include AGIX, NTX, FET, WMTx, RJV and CGV.
The bridge uses a burn-and-mint model. When supported tokens move from Ethereum to Cardano, tokens are burned on Ethereum and an equivalent amount is minted on Cardano. Transfers in the opposite direction burn the Cardano-side tokens before corresponding tokens are minted on Ethereum.
This design means authorization over token creation is security-critical. If the authority used to validate legitimate cross-chain activity is compromised, unauthorized supply can potentially be created even though the underlying Ethereum and Cardano networks continue functioning normally.
Unauthorized AGIX, WMTx, NTX and CGV Issuance
Early monitoring during the developing incident identified smaller snapshots of unauthorized AGIX and WMTx issuance. More comprehensive subsequent blockchain analysis produced a significantly larger picture.
Bitquery measured approximately 895.96 million AGIX, 500.48 million WMTx, 408.53 million NTX and 492.40 million CGV created during the incident. It separately recorded approximately 8.72 million FET removed from the Fetch.ai conversion contract.
The mechanisms were not identical across every asset. Bitquery's reconstruction indicates that the FET movement involved funds transferred from a converter, while unauthorized token creation occurred through different minting or converter mechanisms for the other assets.
This distinction matters because the number of tokens created does not represent the amount of money successfully extracted by the attacker. Unauthorized supply, available liquidity, realized sales and actual project or user losses are different measurements.
How the WMTx Bridge Was Designed
WMTx had previously been integrated into SingularityNET's multi-token bridge to support transfers between Ethereum and Cardano.
In its official announcement of the World Mobile integration, SingularityNET explained that the Ethereum-side implementation involved a smart contract receiving a “Minter role,” allowing the minting and burning operations required by the bridge.
The same documentation says SingularityNET's backend handled events across both sides of the bridge and performed calculations and security checks while World Mobile used the infrastructure for WMTx transfers.
That architecture provides important context for why compromised authorization can have consequences for token supply without implying that Ethereum or Cardano themselves were exploited.
Fetch.ai Says Its Contracts Are Not Under Threat
The attribution is particularly important because the first major observable asset movement involved FET.
Fetch.ai's subsequent incident update said its contracts were not currently under threat and shifted attention toward SingularityNET infrastructure. Fetch.ai also took precautionary measures around connected bridge and conversion functionality while the investigation continued.
The distinction prevents the event from being inaccurately described simply as a “Fetch.ai hack.” FET activity forms part of the incident chronology, but the developing evidence indicates a wider compromise spanning infrastructure and authorization associated with multiple projects.
How FET and NTX Fit Into the Attack Sequence
The earlier FET and NTX activity remains important because it helps reconstruct how the wider incident unfolded.
Bitquery recorded approximately 8.72 million FET leaving the relevant conversion contract on September 19. Its investigation says the FET was subsequently swapped, returning approximately 523 ETH.
Approximately 408.53 million NTX were then created. Bitquery's analysis distinguishes the NTX event from the converter activity affecting some of the other assets, reporting that the attacker called the mint function on the NTX token contract itself.
The subsequent AGIX, WMTx and CGV activity broadened the incident from an isolated asset event into a multi-project security problem involving token issuance and cross-chain infrastructure.
Why the Token Values Are Not the Same as Losses
The scale of unauthorized issuance can produce very large theoretical valuations when token quantities are multiplied by market prices. That approach can be misleading in a security incident.
Newly created unauthorized tokens are not automatically equivalent to money extracted from an ecosystem. Available market liquidity can be far smaller than the nominal value of the supply, some tokens may never be sold, and market prices can change sharply as an incident becomes public.
Bitquery's later investigation separates the counterfeit supply from proceeds generated through sales and other asset movements. TCP therefore does not use the nominal value of the unauthorized token supply as a confirmed theft or victim-loss figure.
The Incident Highlights Authorization-Key Risk
The incident also highlights a security property that can be easy to overlook when evaluating cross-chain systems: the security of the smart contract is only one part of the system.
Bridge operations can depend on privileged authorization capable of confirming that an event occurred on another network. A valid privileged signature may cause a contract to perform an operation exactly as designed even when the underlying authorization has been compromised.
Bitquery's analysis attributes the unauthorized activity to project signing and minting credentials rather than identifying a conventional smart-contract bug that allowed an arbitrary user to bypass contract logic.
A final project-level technical post-mortem will still be necessary to establish the complete compromise path, operational failures and remediation measures.
This Was Not an Ethereum or Cardano Exploit
Nothing in the evidence currently available establishes that Ethereum's or Cardano's consensus protocols were compromised.
The affected systems sit above those underlying networks. Ethereum and Cardano executed transactions presented to them according to their respective protocol rules; the security problem concerns the authorization and application infrastructure controlling token issuance and cross-chain operations.
Describing the event as an Ethereum or Cardano hack would therefore misrepresent the current evidence.
What Is Confirmed and What Remains Unknown
On-chain evidence establishes significant unauthorized token issuance across several assets and the movement of FET from conversion infrastructure. The incident has also triggered precautionary and recovery actions across the affected ecosystem.
Several material questions remain unresolved.
- A final joint technical post-mortem explaining the complete compromise path has not been published.
- The affected projects have not yet produced a single final reconciliation covering all unauthorized supply and its treatment across every relevant network.
- Unauthorized token issuance should not be treated as equivalent to realized financial loss.
- The final recovery treatment for affected token supply remains important to establish.
- Additional details about credential rotation, minting authority and bridge restoration may emerge as the investigation progresses.
What Users Should Do
- Follow official project channels for bridge, conversion, snapshot and token-status updates.
- Avoid unofficial recovery services, migration websites or unsolicited support accounts claiming to resolve the incident.
- Never provide seed phrases, private keys or authentication credentials to anyone claiming to assist with recovery.
- Exercise caution with unusual token deposits or transactions connected to the affected assets while recovery work continues.
- Do not interpret the incident as evidence that Ethereum or Cardano themselves have been compromised.
Why It Matters
The incident demonstrates how shared cross-chain infrastructure can turn a security failure into a multi-project event.
A bridge with privileged authority over token issuance carries a different risk profile from a simple transfer interface. If critical authorization is compromised, the contracts may perform operations that appear technically valid while creating supply that was never backed by the corresponding cross-chain action.
The scope is particularly significant because multiple assets were affected rather than a single isolated token. That makes the eventual technical post-mortem important not only for the projects directly involved but also for other protocols relying on privileged signing systems for cross-chain operations.
What to Watch Next
- A final technical post-mortem from SingularityNET and the other affected teams.
- A reconciled accounting of unauthorized AGIX, WMTx, NTX and CGV supply across affected networks.
- Confirmation that compromised signing, minting and other privileged credentials have been revoked or replaced.
- Recovery plans addressing unauthorized token supply that reached other networks or trading venues.
- Restoration of paused bridge and conversion functions.
- Final accounting that distinguishes realized proceeds, recovered assets, counterfeit token supply and actual project or user losses.
The Bottom Line
The security incident first visible through FET and NTX activity has developed into a broader multi-project event involving SingularityNET-linked cross-chain and authorization infrastructure.
On-chain analysis has identified large unauthorized issuance across AGIX, WMTx, NTX and CGV alongside the earlier FET movement. The quantities involved are significant, but unauthorized token supply must be distinguished from assets actually sold, realized attacker proceeds and final victim losses.
Fetch.ai says its own contracts are not currently under threat. The investigation and recovery process remains active, and the full impact will not be settled until the affected projects publish a final technical explanation and reconcile the unauthorized supply across networks.
Responses (0 )