


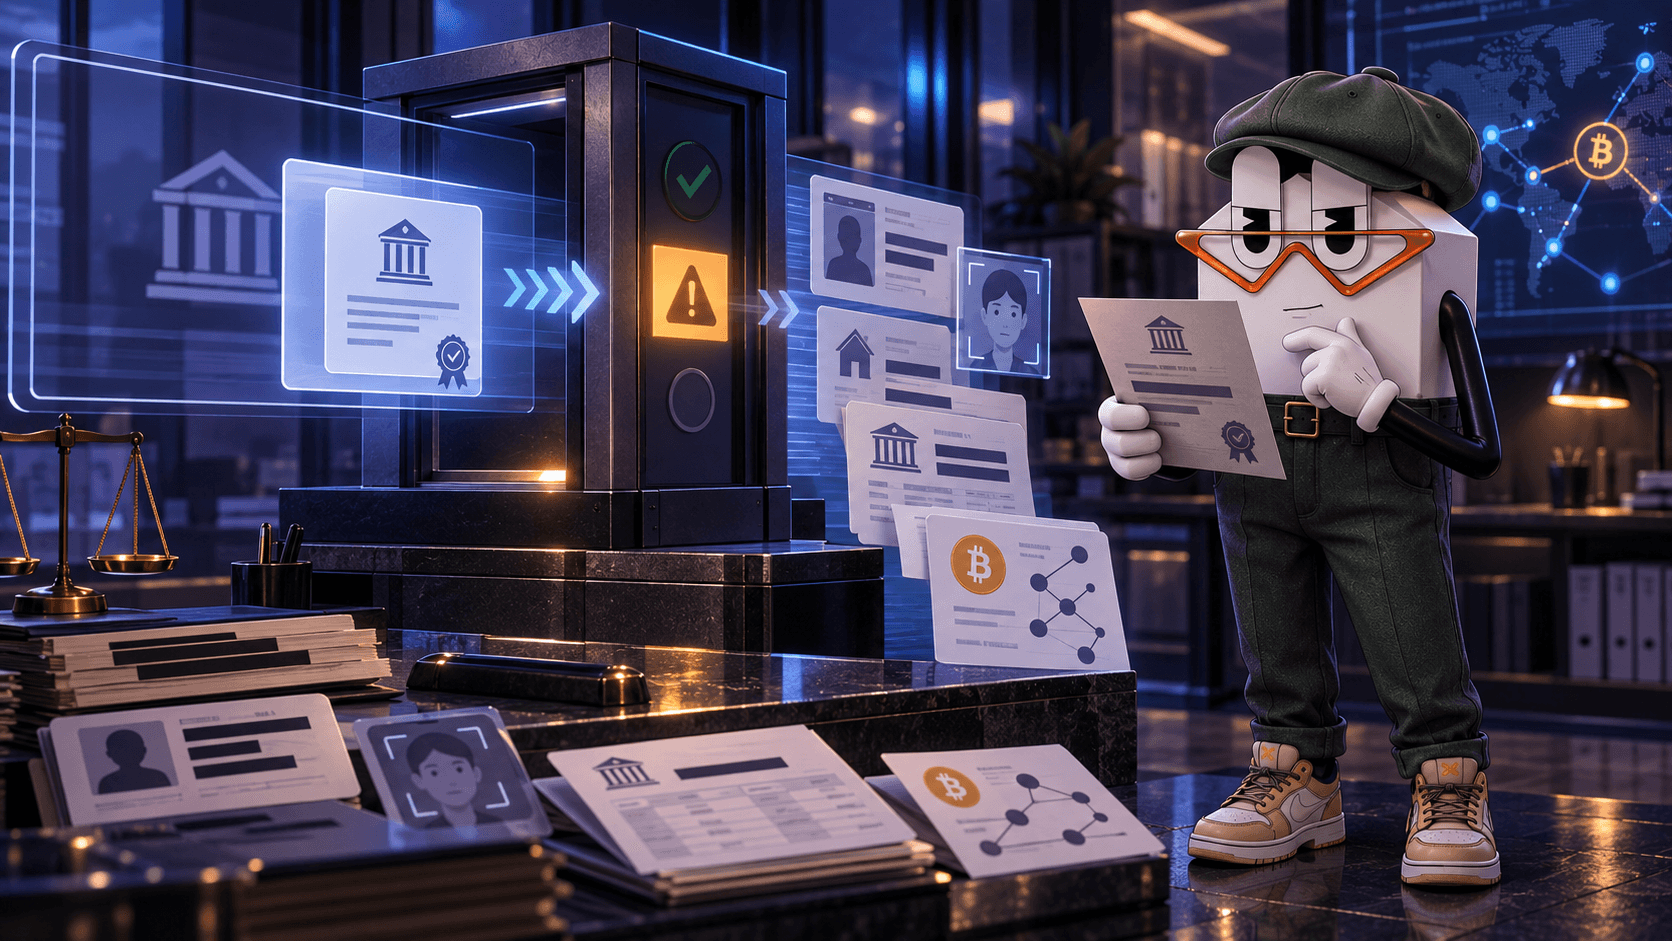
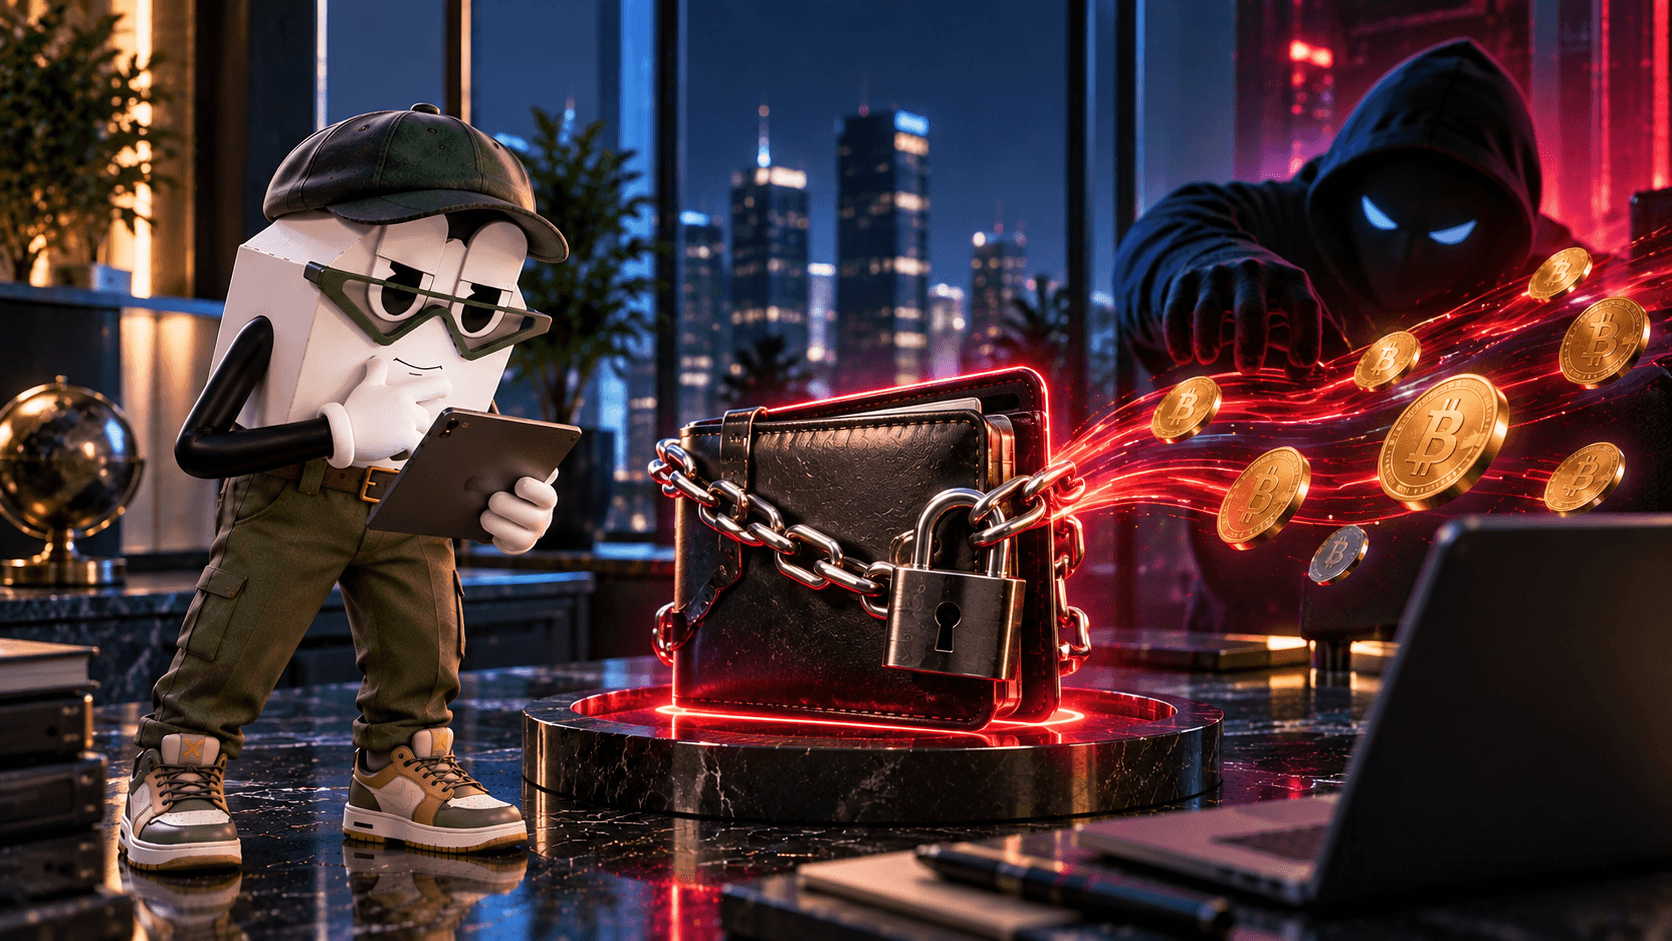
The Revolut customer-data incident has escalated into a public extortion campaign. A group calling itself “iamnotavillain” has publicly demanded 6,000 Monero (XMR), worth roughly $3 million at the time of the demand, and threatened to sell compromised customer records to other criminal groups if payment is not made within 24 hours. Revolut says it has received no direct contact or ransom demand from the people claiming responsibility.
The new threat follows Revolut’s disclosure that sensitive personal and financial records were released after fraudulent information requests arrived through a legitimate government-agency email channel. Reporting now indicates that approximately 680 customers were affected. Revolut continues to say that its core systems and customer funds were not compromised.
Latest Update — September 17, 2026
Reuters reported that Revolut has received no direct contact or ransom demand from the individuals or group claiming responsibility for the customer-data incident, despite a public extortion demand appearing online.
The group calling itself “iamnotavillain” publicly demanded 6,000 XMR, valued at approximately $3 million when the demand was reported, and set a 24-hour deadline. The group threatened to sell compromised customer information to other criminal organizations if the demand was not met.
The Financial Times reported that the ultimatum was posted publicly alongside a countdown clock. The demand represents a new stage in the incident, but the group’s claims and threats should not be treated as independently confirmed statements from Revolut.
The distinction is important: there is now a public ransom claim connected to the incident, but Revolut says the people claiming responsibility have not directly contacted the company or delivered a ransom demand to it.
Italian authorities are also investigating how an official government communication channel was abused. ANSA reported that Italian postal police opened an investigation after customer information was obtained through requests reportedly sent from a legitimate Italian government email account.
Key Findings
- A group calling itself “iamnotavillain” has publicly demanded 6,000 XMR, worth roughly $3 million when reported, and threatened to sell compromised Revolut customer records after a 24-hour deadline.
- Revolut says it has received no direct contact or ransom demand from the people claiming responsibility for the incident.
- Reporting indicates that approximately 680 customers were affected by the underlying disclosure.
- The exposed material includes sensitive identity and financial information, including identity documents, addresses, account information and transaction histories.
- Revolut says its core systems and customer funds were not compromised. The incident resulted from fraudulent information requests sent through a legitimate government communication channel rather than penetration of Revolut’s banking infrastructure.
- Italian authorities are investigating the abuse of the government email channel used in the incident.
What Happened
Revolut originally characterized the event as an external impersonation attack. An unauthorized party submitted fraudulent requests for customer information using an email address associated with a legitimate government-agency domain, making the requests appear authentic.
Revolut confirmed the underlying incident after affected customers were notified that personal information had been disclosed to an unauthorized third party. The company said a limited number of customers were affected and that its systems and customer funds remained secure.
Subsequent reporting placed the number of affected customers at approximately 680 and linked the fraudulent requests to a compromised Italian government communication channel. The exposed information reportedly included identity documents, addresses, account details and Bitcoin transaction records.
Revolut said it blocked the sender after detecting the issue and alerted the relevant government agency, law-enforcement bodies, data-protection authorities and financial regulators.
Blockchain investigator ZachXBT drew attention to the incident through an incident record posted on Telegram. An affected user, Marc Zeller, also discussed the disclosure publicly on X.
The Incident Has Escalated Into Public Extortion
The September 17 development changes the immediate risk surrounding the incident. The people claiming responsibility are no longer only associated with obtaining customer records; they are now publicly threatening to distribute or sell those records unless a cryptocurrency payment is made.
The group’s demand for 6,000 XMR was worth approximately $3 million when reported. The demand was accompanied by a 24-hour deadline and a threat to sell the customer information to other criminal groups.
That does not mean Revolut has acknowledged receiving or negotiating over the demand. Revolut explicitly told Reuters that it had received no direct contact or ransom demand from the individuals or group claiming responsibility.
The public threat nevertheless increases the potential consequences for affected customers because identity documents, contact information and financial histories could become useful to additional criminal actors if the records are redistributed.
What Data May Have Been Disclosed
Customer notices and subsequent reporting identified potentially exposed information including passports or driving licenses, home addresses, account information, verification selfies, account statements and transaction histories.
Those categories do not necessarily mean every affected customer had every type of record disclosed. Revolut has not published a customer-by-customer breakdown of the information involved.
A verification selfie is also distinct from biometric facial telemetry. Revolut previously said biometric data was not exposed, while customer notices reportedly identified selfie images among information that may have been shared. An image can still create impersonation risks even when a mathematical biometric template was not disclosed.
What Revolut Says Was Not Affected
Revolut says its internal systems and customer funds were unaffected. There is no evidence from the company’s statements that the attackers penetrated Revolut’s core banking infrastructure in order to obtain the customer records.
The records were instead released in response to fraudulent external information requests that appeared to originate through a legitimate government communication channel.
The Bitcoin network was not compromised either. Bitcoin transaction histories associated with customer accounts can create serious privacy risks when linked to verified identities, but their exposure does not indicate a failure of Bitcoin’s consensus or network security.
Why Crypto-Heavy Customers Face Additional Risk
The incident carries an additional risk for customers whose identities can be connected to significant cryptocurrency activity.
The Financial Times reported that the people claiming responsibility said they used blockchain activity to target customers with substantial cryptocurrency exposure. Their account of how targets were selected remains an attacker claim, but it highlights why linking KYC records to crypto transaction histories can be particularly sensitive.
Identity documents, a home address and transaction records can give criminals enough contextual information to construct highly personalized phishing, impersonation or extortion attempts. Knowledge that a particular person may control substantial crypto assets can also increase personal-security concerns.
These risks should not be confused with confirmed outcomes. Public reporting does not establish that every affected customer was deliberately selected for crypto holdings or that affected users have subsequently lost cryptocurrency because of the disclosure.
Italian Authorities Are Investigating
The investigation now extends beyond Revolut and UK authorities because the fraudulent requests have been linked in reporting to an Italian government email channel.
Italian postal police opened an investigation into the incident, while reporting has identified the certified government email account involved as being associated with authorities in Reggio Calabria. Italian prosecutors are also examining the case.
The investigation is important because the unanswered security question is not simply why Revolut accepted the requests. Authorities also need to establish how a legitimate government communication channel came to be used by an unauthorized party and whether the problem extended beyond the requests sent to Revolut.
What Affected Users Should Do Now
- Treat unexpected calls, emails or messages referencing Revolut, identity checks, account balances or past crypto transfers as untrusted even when they contain accurate personal information.
- Open the Revolut app or official website directly rather than following links in unsolicited messages, and independently verify requests claiming to come from Revolut or law enforcement.
- Secure the email account connected to Revolut with a unique password and multi-factor authentication, and review recovery methods and forwarding rules for unauthorized changes.
- Monitor financial accounts and known crypto addresses for unexpected activity, while recognizing that exposure of transaction history does not itself give an attacker control over a wallet.
- Affected users whose home addresses or identity documents were exposed should preserve Revolut’s notification and follow case-specific guidance from the company, law enforcement or the relevant data-protection authority.
- Users with significant publicly traceable cryptocurrency holdings should be particularly cautious about highly personalized phishing, impersonation and extortion attempts that reference accurate transaction information.
What Remains Unknown
Several important parts of the incident remain unresolved.
The identity of the people behind the operation has not been established publicly. The group calling itself “iamnotavillain” claims responsibility, but investigators have not publicly attributed the incident to that group.
It also remains unclear precisely how the legitimate Italian government communication channel was compromised or abused, how long unauthorized requests were being submitted and whether the same channel was used to obtain information from other financial institutions.
The public ransom threat also creates another unresolved question: whether the compromised customer records will be published, sold or otherwise distributed. The group has threatened to do so, but a threat is not evidence that a sale or wider distribution has already occurred.
Revolut’s statement that it has received no direct contact from the people claiming responsibility also means the public 6,000-XMR demand should continue to be described as an attacker claim rather than a ransom negotiation confirmed by the company.
What to Watch Next
- Whether the group claiming responsibility publishes or attempts to sell additional customer records after its public deadline.
- Whether Revolut reports receiving any direct communication from the people behind the extortion campaign.
- Findings from Italian investigators on how the government email channel was compromised or abused.
- Any additional findings from UK data-protection or financial regulators investigating the disclosure.
- Whether evidence emerges that other institutions received fraudulent information requests through the same compromised channel.
The Bottom Line
The Revolut incident has moved from an unauthorized customer-data disclosure into an active public extortion stage. A group claiming responsibility has demanded 6,000 XMR, worth roughly $3 million when reported, and threatened to sell compromised customer records after a 24-hour deadline.
But two distinctions remain essential. Revolut says it has received no direct ransom demand from the people claiming responsibility, and the incident was not a reported penetration of Revolut’s core infrastructure. Customer funds remain unaffected according to the company.
The immediate concern is therefore the potential misuse or wider distribution of sensitive identity and financial records belonging to approximately 680 customers, particularly where those records can connect verified identities with cryptocurrency activity. The next material developments will come from the extortion campaign itself and the investigations into how a legitimate government communication channel was used to obtain the data.
Responses (0 )